
Table of Contents
Pages
- ADHICS Compliance UAE — Abu Dhabi Healthcare Cybersecurity
- Mobile Application Penetration Testing UAE | OWASP MASVS | iOS & Android
- AWS Security Services Dubai | Amazon Cloud Security UAE | eSHIELD IT Services
- Cybersecurity for Startups & SMEs Dubai | Affordable Security | eSHIELD IT Services
- Healthcare Cybersecurity UAE | ADHICS, DHA, DOH Compliance | eSHIELD IT Services
- Banking & Financial Services Cybersecurity Dubai | CBUAE, PCI DSS, DFSA | eSHIELD IT Services
- External Attack Surface Management UAE | EASM Services Dubai | eSHIELD IT Services
- DESC ISR Compliance Dubai | ISR v3 Audit & Implementation | eSHIELD IT Services
- Azure Security Services Dubai | Microsoft Cloud Security UAE | eSHIELD IT Services
- Cybersecurity Company Sydney, Australia | ASD Essential Eight & ISO 27001 | eShield IT
- Cybersecurity Company Delhi, India | Government, IT & DPDP Act Compliance | eShield IT
- Cybersecurity Company Mumbai, India | RBI, SEBI & IRDAI Compliance | eShield IT
- Cybersecurity Company Bangalore, India | VAPT, ISO 27001 & DPDP Act Compliance
- Cybersecurity Company Doha, Qatar | NIA, QFCRA & NISCF Compliance | eShield IT
- Cybersecurity Company Riyadh, Saudi Arabia | NCA ECC & SAMA Compliance | eShield IT
- Cybersecurity Company Abu Dhabi | NESA, ADGM & ADSIC Compliance | eShield IT
- Oil & Gas Cybersecurity UAE | ADNOC Suppliers & Offshore OT Security
- Cybersecurity for Education Sector UAE | Schools, Universities & EdTech Security
- Manufacturing & Industrial Cybersecurity UAE | OT/ICS Security & IEC 62443
- Cybersecurity UAE: Complete FAQ Guide | eShield IT Services
- Red Team vs Penetration Testing: What Does Your UAE Business Need? | eShield IT
- SOC 2 vs ISO 27001: Which Does Your UAE Business Need? | eShield IT
- PCI DSS vs ISO 27001: Key Differences Explained | eShield IT UAE
- Retail & eCommerce Cybersecurity UAE | PCI DSS, Fraud Prevention & App Security
- Government Cybersecurity Services UAE | NESA, NCA ECC & Critical Infrastructure Protection
- Get Free Cybersecurity Consultation — eShield IT UAE
- Cyber Security Services in Morocco | CNDP Law 09-08, DGSSI & BAM | eShield IT
- Cyber Security Services in Ghana | Ghana DPA, Bank of Ghana & Cybersecurity Act | eShield IT
- Cyber Security Services in Egypt | Egypt PDPL, CBE & NTRA Compliance | eShield IT
- Cyber Security Services in Nigeria | NDPA 2023, CBN & NITDA Compliance | eShield IT
- Cyber Security Services in Kenya | Kenya DPA 2019 & CBK Compliance | eShield IT
- Cyber Security Services in South Africa | POPIA, SARB & ISO 27001 | eShield IT
- Cyber Security Services in Africa | eShield IT Services
- Cyber Security Services in Kuwait | CBK Technology Risk, CITRA & ISO 27001 | eShield IT
- Cyber Security Services in Bahrain | CBB TRM, Bahrain PDPL & ISO 27001 | eShield IT
- Cyber Security Services in Oman | ITA Framework, PDPL & ISO 27001 | eShield IT
- UAE PDPL Compliance Services 2027 — Personal Data Protection Law | eShield IT
- Cybersecurity GRC UAE | Governance Risk Compliance Dubai
- Managed Security Services UAE | MSSP Dubai | eShield IT
- Cybersecurity Audit UAE | IT Security Assessment Dubai
- Ransomware Protection Services in UAE
- Get Free Digital Marketing Strategy
- B2B Lead Generation Agency Dubai | Sales Pipeline UAE
- Performance Marketing Agency Dubai | ROI-Driven UAE Marketing
- Content Marketing Agency Dubai | Content Strategy UAE
- PPC Agency Dubai | Google Ads Management UAE
- Social Media Marketing Agency Dubai | SMM Services UAE
- Digital Marketing Agency Dubai | UAE Digital Marketing Services
- SEO Agency Dubai | Best SEO Company in UAE
- Kumar — Lead Security Consultant & Principal Author
- Editorial & Content Standards
- About eShield IT Services | Cybersecurity Experts
- VAPT Services in Dubai & UAE — Vulnerability Assessment & Penetration Testing
- KSA PDPL implementation and Fines
- Virtual CISO Services (vCISO) — Fractional Chief Information Security Officer
- Cybersecurity Services in Dubai, UAE
- Security Maturity Assessment UAE — Measure & Improve Your Cyber Posture
- Audit & Compliance Services UAE
- Cybersecurity Services in Dubai & UAE
- Cyber Security Services in India | eShield IT
- Cyber Security Framework SAMA
- Information Security Awareness Training (ISAT) — Managed Service & Phishing Simulations UAE
- Australia
- NESA Audit UAE | NESA Compliance Consultants | eShield IT
- SOC2 Audit
- Cyber Security Services in Qatar | NIA Certification, NISCF & QFC Compliance | eShield IT
- Cyber Security Services in Saudi Arabia | SAMA, NCA ECC & PDPL Compliance | eShield IT
- Geographies
- Privacy Policy
- Penetration Testing Services in Dubai & UAE
- Managed SOC Services UAE | 24/7 Security Operations Center
- Threat Hunting Services in Dubai & UAE | eShield IT
- Digital Forensics Services Dubai & UAE | Computer & Cyber Forensics | eShield IT
- Malware Analysis Services in Dubai & UAE | eShield IT
- Cloud Security Services in Dubai & UAE | eShield IT
- Incident Response Services in Dubai & UAE | eShield IT
- Red Team Assessment Services in Dubai & UAE — Adversarial Attack Simulation
- Mobile Application Audits
- ISO 27001 Certification Consulting in Dubai, UAE
- Cybersecurity Company in UAE | eShield IT Services Dubai
- Vulnerability Assessment Services in Dubai & UAE — Network, Web & Cloud
- Application Security Auditing
- PCI DSS Compliance Services Dubai UAE | eShield IT
- Contact eShield IT Services
- Information Security Blogs
- Home
Categories
- What is Cyber Security?
- Web Application Security
- Web Apllications Security
- wapt
- Vulnerability Testing and Penetration Testing
- Vulnerability Scanning
- vulnerability assessment and penetration testing
- vCISO
- vapt
- Useful
- Uncategorized
- UAE Cyber Security Company
- top cyber security companies in the UAE
- SOC UAE
- SOC 2 Certification Cost
- Security
- Red Teaming Services
- Red teaming
- Race Condition
- Privacy
- Pentest
- Penetration Testing
- PCI DSS Stands for
- PCI DSS Requirements
- PCI DSS Meaning
- PCI DSS Certification
- PCI DSS
- News
- new tech
- Most Popular SIEM Tools
- Managed Security Services Provider
- ISO 27001 Compliance in the UAE
- General
- cybersecurity regulation
- Cybersecurity
- cyber sercurity firm
- Cyber Security UAE
- Cyber Security Specialist
- Cyber Security Services
- cyber security master
- Cyber Security Jobs in Dubai
- cyber security in UAE
- Cyber Security GRC
- cyber security course
- Cyber Security Consultant
- Cyber Security Company in Dubai
- Cyber Security Company Dubai
- Cyber Security Basic
- Cyber Security Awareness
- Cyber Security
- Compliance
- AI-Powered Cybersecurity
What Should Businesses Check During a Web Application Security Assessment?
What Should Businesses Check During a Web Application Security Assessment?
Today, protecting online assets is a top priority for companies in the United Arab Emirates. A web application security assessment gives a practical, step-by-step review of your current digital controls.
How Does a vCISO Help Businesses Manage Cybersecurity Risks?
How Does a vCISO Help Businesses Manage Cybersecurity Risks?
In the United Arab Emirates’ fast-changing digital landscape, organizations face constant threats to sensitive data. Many companies cannot maintain strong security without the high cost of a full-time executive. This
How Can Businesses Identify Security Weaknesses Before a Cyberattack?
How Can Businesses Identify Security Weaknesses Before a Cyberattack?
Across the United Arab Emirates, organizations face constant threats from sophisticated cybercriminals. Standard firewalls cannot fully protect sensitive data. Proactive defense strategies help businesses stay ahead of malicious actors scanning
How Can Businesses Identify Security Gaps in Their Web Applications?
How Can Businesses Identify Security Gaps in Their Web Applications?
Digital transformation in the United Arab Emirates has opened major growth opportunities. Yet, this fast expansion exposes organizations to advanced cyber threats aimed at web portals and APIs. Proactive defense
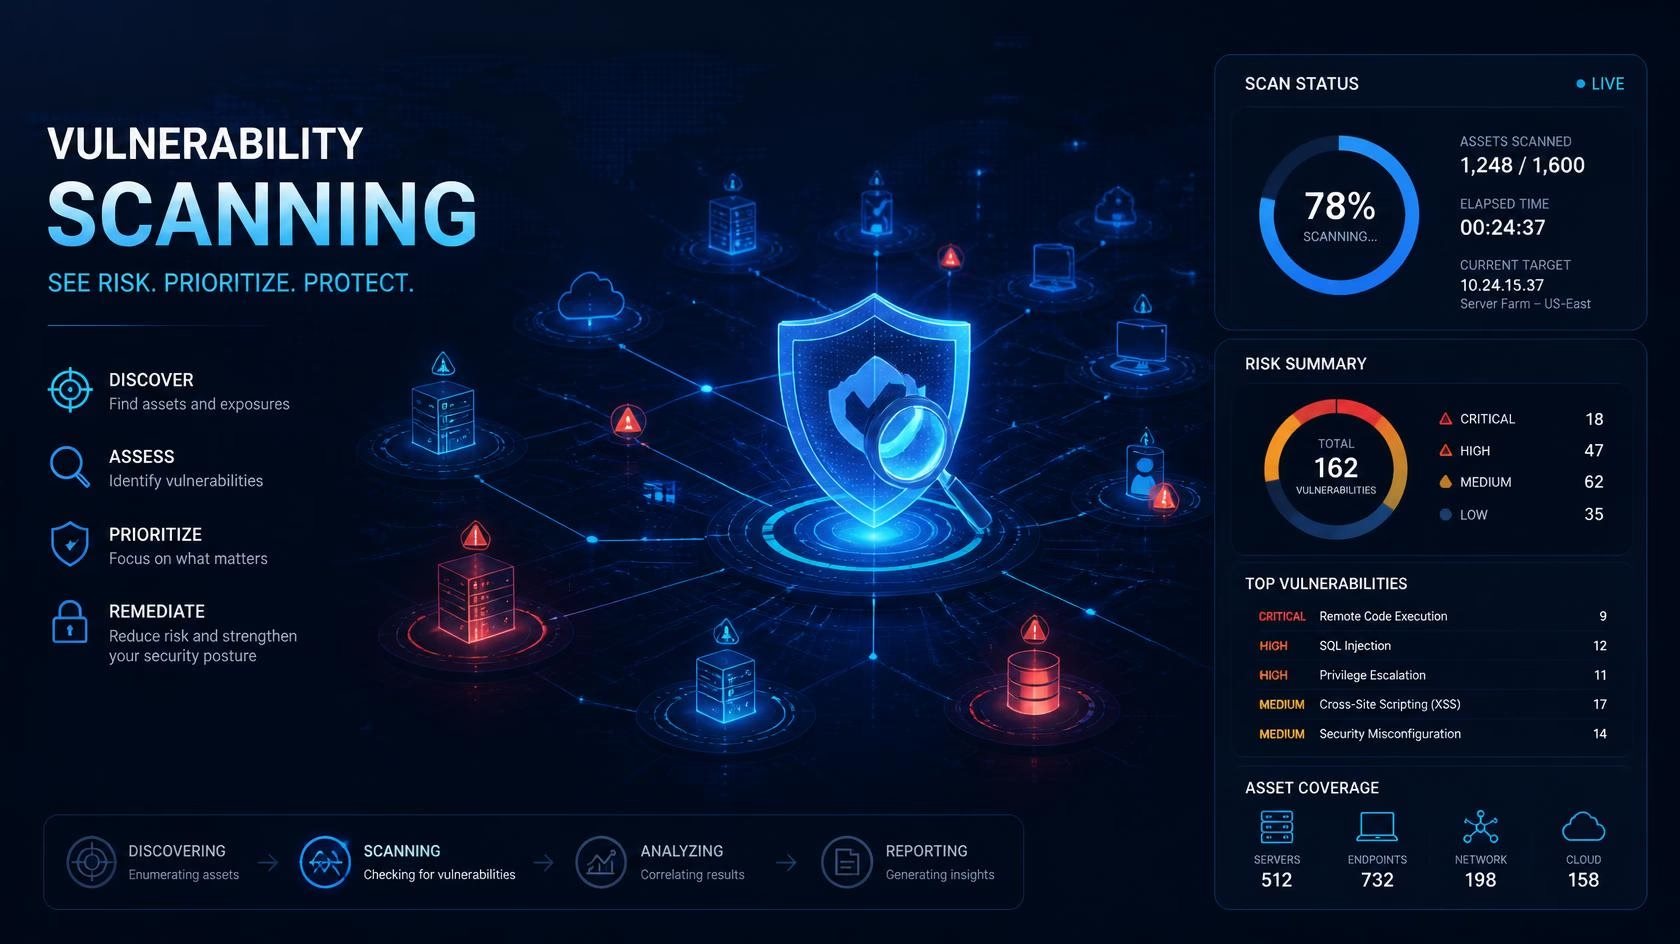
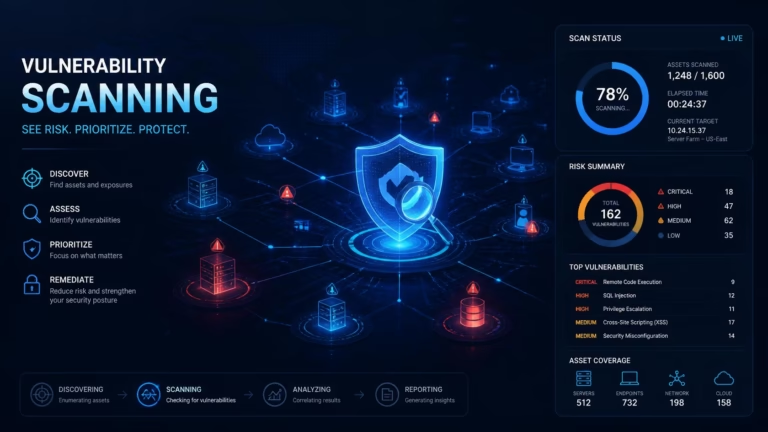
How to Run Vulnerability Scanning with Eshielditservices
How to Run Vulnerability Scanning with Eshielditservices
Protecting corporate assets in the United Arab Emirates requires a proactive mindset in today’s fast-changing digital world. Many businesses treat security checks as a one-time event, but true safety needs
In today’s digital landscape, understanding and effectively implementing cybersecurity measures have become paramount for organizations of all sizes. Among the many frameworks available to enhance cybersecurity posture, the National Institute of Standards and Technology (NIST) Risk Management Framework (RMF) stands out as a comprehensive guide for managing cybersecurity risks. This article delves into the intricacies of navigating the NIST RMF to bolster information security and safeguard critical assets.
Understanding the NIST Risk Management Framework
What is the NIST Risk Management Framework?
The NIST RMF is a structured approach that assists organizations in managing their cybersecurity risks. It provides a set of processes and activities to help organizations categorize their information systems, select appropriate security controls, and monitor the effectiveness of these controls.
How does the NIST RMF enhance cybersecurity?
By following the NIST RMF, organizations can establish a robust cybersecurity posture based on risk management activities. This proactive approach enables organizations to identify, assess, and mitigate cybersecurity risks effectively, thereby enhancing their overall security resilience.
Key components of the NIST RMF
The NIST RMF comprises several key components, including risk assessment, security control selection, security control implementation, security control assessment, and security control monitoring. These components work together to help organizations effectively manage cybersecurity risks and maintain a secure environment.
Implementing the NIST Cybersecurity Framework
Steps to implement the NIST Cybersecurity Framework
Implementing the NIST Cybersecurity Framework involves several steps, such as identifying and prioritizing critical assets, aligning security controls with NIST guidelines, and continuously monitoring and updating security measures to address emerging threats.
Benefits of aligning with NIST cybersecurity guidelines
Aligning with NIST cybersecurity guidelines offers numerous benefits, including enhanced security posture, improved resilience against cyber threats, regulatory compliance, and increased stakeholder trust and confidence in the organization’s security practices.
Common challenges in implementing NIST cybersecurity measures
While implementing NIST cybersecurity measures is essential, organizations may face challenges such as resource constraints, lack of cybersecurity expertise, and evolving threat landscapes. Overcoming these challenges requires a proactive and holistic approach to cybersecurity management.
Risk Management in Critical Infrastructure
Why is risk management crucial for critical infrastructure?
Risk management is crucial for critical infrastructure as any disruptions can have far-reaching impacts on public safety, national security, and the economy. By proactively managing risks, organizations can prevent or minimize the impact of potential cyber threats.
Role of the NIST RMF in safeguarding critical infrastructure
The NIST RMF plays a vital role in safeguarding critical infrastructure by offering tailored guidance and security controls to address unique risks in sectors such as energy, transportation, and healthcare. Organizations can leverage the NIST RMF to enhance their cybersecurity readiness and resilience.
Addressing unique risks in critical infrastructure through NIST guidelines
NIST guidelines help critical infrastructure entities identify and mitigate sector-specific risks such as supply chain vulnerabilities, aging legacy systems, and interconnected dependencies. By adhering to NIST guidelines, organizations can strengthen their cybersecurity defenses and protect critical assets.
Enterprise Risk Management with NIST Framework
Integrating NIST guidelines into enterprise risk management
Integrating NIST guidelines into enterprise risk management allows organizations to align their cybersecurity efforts with overall risk management practices. By adopting a cohesive approach, organizations can effectively manage cybersecurity risks while enhancing their enterprise-wide resilience.
Leveraging the NIST framework for comprehensive risk management
The NIST framework provides a comprehensive approach to risk management, encompassing both cybersecurity and overall enterprise risks. By leveraging the NIST framework, organizations can identify interdependencies, prioritize risks, and implement proactive measures to mitigate potential threats.
Best practices for enterprise risk management according to NIST
NIST emphasizes the importance of continual risk assessment, stakeholder engagement, information sharing, and response planning in enterprise risk management. Following these best practices can help organizations enhance their risk management capabilities and adapt to evolving cybersecurity challenges.
Enhancing Information Security through NIST Guidelines
How NIST guidelines help organizations categorize sensitive information
NIST guidelines provide a structured approach for organizations to categorize sensitive information based on its impact and criticality. By categorizing information effectively, organizations can apply appropriate security controls and safeguard sensitive data from unauthorized access or disclosure.
Implementing NIST practices to safeguard information security
Implementing NIST practices enables organizations to strengthen their information security posture by adopting industry-recognized security controls, best practices, and risk management processes. This proactive approach helps organizations stay ahead of emerging threats and protect their valuable information assets.
Utilizing artificial intelligence in alignment with NIST cybersecurity recommendations
Artificial intelligence (AI) can enhance cybersecurity capabilities by automating threat detection, incident response, and risk analysis processes. When aligned with NIST cybersecurity recommendations, AI technologies can help organizations improve their incident response times, enhance threat intelligence, and bolster overall security resilience.