
Table of Contents
Pages
- ADHICS Compliance UAE — Abu Dhabi Healthcare Cybersecurity
- Mobile Application Penetration Testing UAE | OWASP MASVS | iOS & Android
- AWS Security Services Dubai | Amazon Cloud Security UAE | eSHIELD IT Services
- Cybersecurity for Startups & SMEs Dubai | Affordable Security | eSHIELD IT Services
- Healthcare Cybersecurity UAE | ADHICS, DHA, DOH Compliance | eSHIELD IT Services
- Banking & Financial Services Cybersecurity Dubai | CBUAE, PCI DSS, DFSA | eSHIELD IT Services
- External Attack Surface Management UAE | EASM Services Dubai | eSHIELD IT Services
- DESC ISR Compliance Dubai | ISR v3 Audit & Implementation | eSHIELD IT Services
- Azure Security Services Dubai | Microsoft Cloud Security UAE | eSHIELD IT Services
- Cybersecurity Company Sydney, Australia | ASD Essential Eight & ISO 27001 | eShield IT
- Cybersecurity Company Delhi, India | Government, IT & DPDP Act Compliance | eShield IT
- Cybersecurity Company Mumbai, India | RBI, SEBI & IRDAI Compliance | eShield IT
- Cybersecurity Company Bangalore, India | VAPT, ISO 27001 & DPDP Act Compliance
- Cybersecurity Company Doha, Qatar | NIA, QFCRA & NISCF Compliance | eShield IT
- Cybersecurity Company Riyadh, Saudi Arabia | NCA ECC & SAMA Compliance | eShield IT
- Cybersecurity Company Abu Dhabi | NESA, ADGM & ADSIC Compliance | eShield IT
- Oil & Gas Cybersecurity UAE | ADNOC Suppliers & Offshore OT Security
- Cybersecurity for Education Sector UAE | Schools, Universities & EdTech Security
- Manufacturing & Industrial Cybersecurity UAE | OT/ICS Security & IEC 62443
- Cybersecurity UAE: Complete FAQ Guide | eShield IT Services
- Red Team vs Penetration Testing: What Does Your UAE Business Need? | eShield IT
- SOC 2 vs ISO 27001: Which Does Your UAE Business Need? | eShield IT
- PCI DSS vs ISO 27001: Key Differences Explained | eShield IT UAE
- Retail & eCommerce Cybersecurity UAE | PCI DSS, Fraud Prevention & App Security
- Government Cybersecurity Services UAE | NESA, NCA ECC & Critical Infrastructure Protection
- Get Free Cybersecurity Consultation — eShield IT UAE
- Cyber Security Services in Morocco | CNDP Law 09-08, DGSSI & BAM | eShield IT
- Cyber Security Services in Ghana | Ghana DPA, Bank of Ghana & Cybersecurity Act | eShield IT
- Cyber Security Services in Egypt | Egypt PDPL, CBE & NTRA Compliance | eShield IT
- Cyber Security Services in Nigeria | NDPA 2023, CBN & NITDA Compliance | eShield IT
- Cyber Security Services in Kenya | Kenya DPA 2019 & CBK Compliance | eShield IT
- Cyber Security Services in South Africa | POPIA, SARB & ISO 27001 | eShield IT
- Cyber Security Services in Africa | eShield IT Services
- Cyber Security Services in Kuwait | CBK Technology Risk, CITRA & ISO 27001 | eShield IT
- Cyber Security Services in Bahrain | CBB TRM, Bahrain PDPL & ISO 27001 | eShield IT
- Cyber Security Services in Oman | ITA Framework, PDPL & ISO 27001 | eShield IT
- UAE PDPL Compliance Services 2027 — Personal Data Protection Law | eShield IT
- Cybersecurity GRC UAE | Governance Risk Compliance Dubai
- Managed Security Services UAE | MSSP Dubai | eShield IT
- Cybersecurity Audit UAE | IT Security Assessment Dubai
- Ransomware Protection Services in UAE
- Get Free Digital Marketing Strategy
- B2B Lead Generation Agency Dubai | Sales Pipeline UAE
- Performance Marketing Agency Dubai | ROI-Driven UAE Marketing
- Content Marketing Agency Dubai | Content Strategy UAE
- PPC Agency Dubai | Google Ads Management UAE
- Social Media Marketing Agency Dubai | SMM Services UAE
- Digital Marketing Agency Dubai | UAE Digital Marketing Services
- SEO Agency Dubai | Best SEO Company in UAE
- Kumar — Lead Security Consultant & Principal Author
- Editorial & Content Standards
- About eShield IT Services | Cybersecurity Experts
- VAPT Services in Dubai & UAE — Vulnerability Assessment & Penetration Testing
- KSA PDPL implementation and Fines
- Virtual CISO Services (vCISO) — Fractional Chief Information Security Officer
- Cybersecurity Services in Dubai, UAE
- Security Maturity Assessment UAE — Measure & Improve Your Cyber Posture
- Audit & Compliance Services UAE
- Cybersecurity Services in Dubai & UAE
- Cyber Security Services in India | eShield IT
- Cyber Security Framework SAMA
- Information Security Awareness Training (ISAT) — Managed Service & Phishing Simulations UAE
- Australia
- NESA Audit UAE | NESA Compliance Consultants | eShield IT
- SOC2 Audit
- Cyber Security Services in Qatar | NIA Certification, NISCF & QFC Compliance | eShield IT
- Cyber Security Services in Saudi Arabia | SAMA, NCA ECC & PDPL Compliance | eShield IT
- Geographies
- Privacy Policy
- Penetration Testing Services in Dubai & UAE
- Managed SOC Services UAE | 24/7 Security Operations Center
- Threat Hunting Services in Dubai & UAE | eShield IT
- Digital Forensics Services Dubai & UAE | Computer & Cyber Forensics | eShield IT
- Malware Analysis Services in Dubai & UAE | eShield IT
- Cloud Security Services in Dubai & UAE | eShield IT
- Incident Response Services in Dubai & UAE | eShield IT
- Red Team Assessment Services in Dubai & UAE — Adversarial Attack Simulation
- Mobile Application Audits
- ISO 27001 Certification Consulting in Dubai, UAE
- Cybersecurity Company in UAE | eShield IT Services Dubai
- Vulnerability Assessment Services in Dubai & UAE — Network, Web & Cloud
- Application Security Auditing
- PCI DSS Compliance Services Dubai UAE | eShield IT
- Contact eShield IT Services
- Information Security Blogs
- Home
Categories
- What is Cyber Security?
- Web Application Security
- Web Apllications Security
- wapt
- Vulnerability Testing and Penetration Testing
- Vulnerability Scanning
- vulnerability assessment and penetration testing
- vCISO
- vapt
- Useful
- Uncategorized
- UAE Cyber Security Company
- top cyber security companies in the UAE
- SOC UAE
- SOC 2 Certification Cost
- Security
- Red Teaming Services
- Red teaming
- Race Condition
- Privacy
- Pentest
- Penetration Testing
- PCI DSS Stands for
- PCI DSS Requirements
- PCI DSS Meaning
- PCI DSS Certification
- PCI DSS
- News
- new tech
- Most Popular SIEM Tools
- Managed Security Services Provider
- ISO 27001 Compliance in the UAE
- General
- cybersecurity regulation
- Cybersecurity
- cyber sercurity firm
- Cyber Security UAE
- Cyber Security Specialist
- Cyber Security Services
- cyber security master
- Cyber Security Jobs in Dubai
- cyber security in UAE
- Cyber Security GRC
- cyber security course
- Cyber Security Consultant
- Cyber Security Company in Dubai
- Cyber Security Company Dubai
- Cyber Security Basic
- Cyber Security Awareness
- Cyber Security
- Compliance
- AI-Powered Cybersecurity
How Does a vCISO Help Businesses Manage Cybersecurity Risks?
How Does a vCISO Help Businesses Manage Cybersecurity Risks?
In the United Arab Emirates’ fast-changing digital landscape, organizations face constant threats to sensitive data. Many companies cannot maintain strong security without the high cost of a full-time executive. This
How Can Businesses Identify Security Weaknesses Before a Cyberattack?
How Can Businesses Identify Security Weaknesses Before a Cyberattack?
Across the United Arab Emirates, organizations face constant threats from sophisticated cybercriminals. Standard firewalls cannot fully protect sensitive data. Proactive defense strategies help businesses stay ahead of malicious actors scanning
How Can Businesses Identify Security Gaps in Their Web Applications?
How Can Businesses Identify Security Gaps in Their Web Applications?
Digital transformation in the United Arab Emirates has opened major growth opportunities. Yet, this fast expansion exposes organizations to advanced cyber threats aimed at web portals and APIs. Proactive defense
How to Run Vulnerability Scanning with Eshielditservices
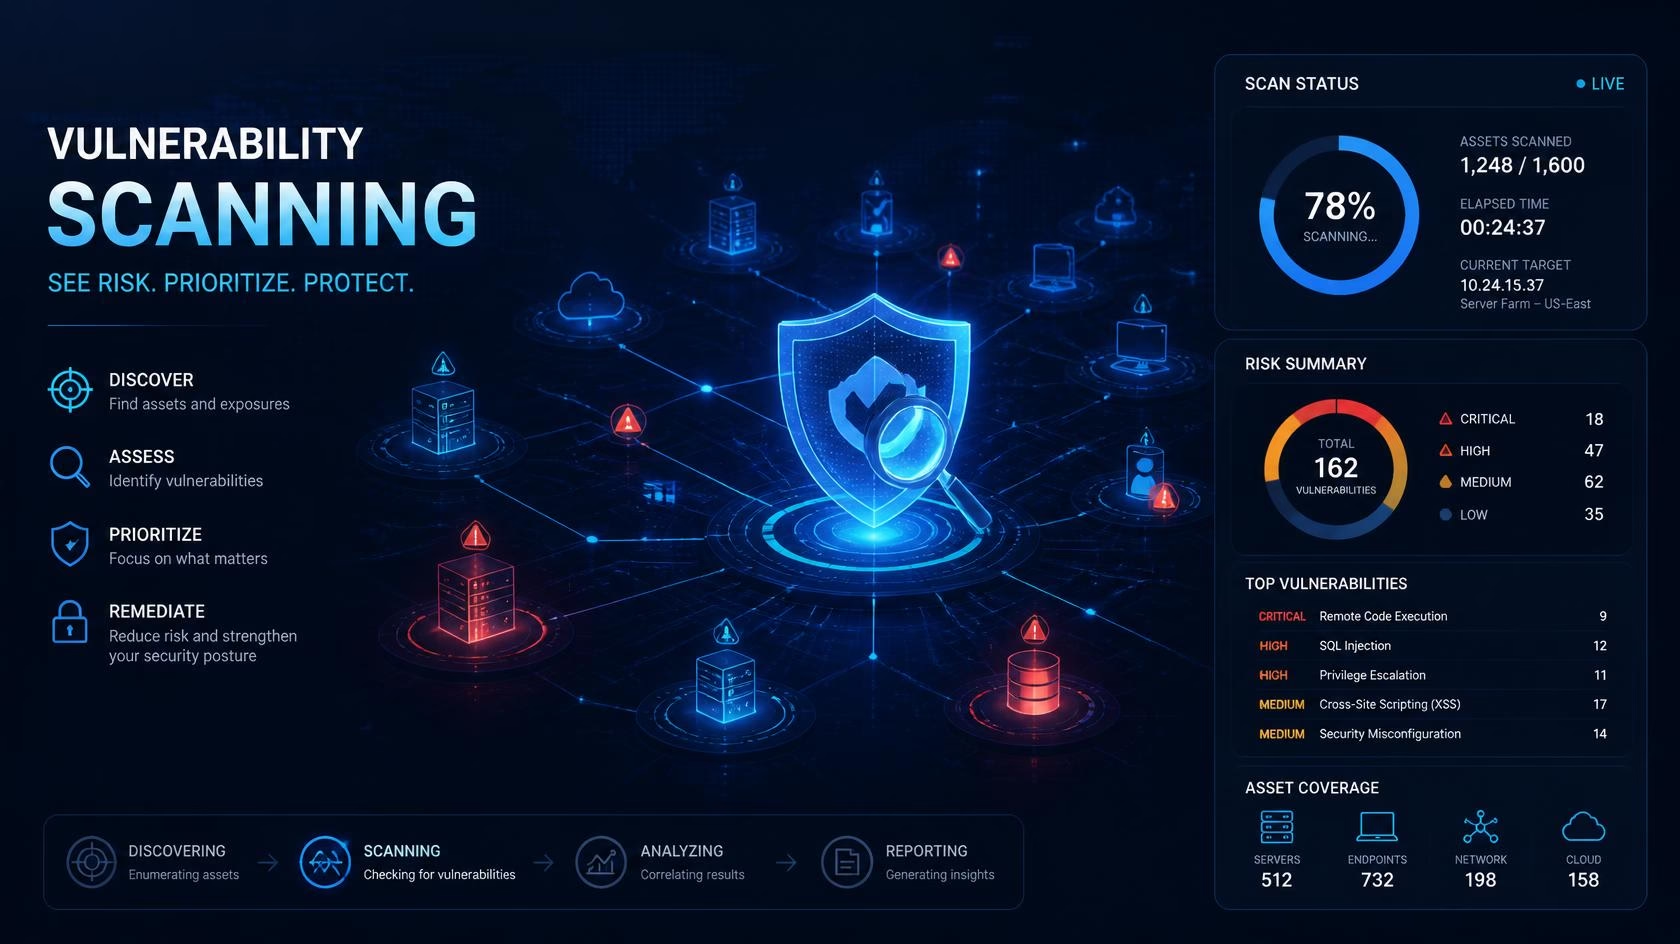
How to Run Vulnerability Scanning with Eshielditservices
Protecting corporate assets in the United Arab Emirates requires a proactive mindset in today’s fast-changing digital world. Many businesses treat security checks as a one-time event, but true safety needs
Continuous Vulnerability Scanning — Why Quarterly Scans Are No Longer Enough
Continuous Vulnerability Scanning — Why Quarterly Scans Are No Longer Enough
Continuous vulnerability scanning is the practice of running automated security scans on an ongoing basis — daily, weekly, or in real time — rather than conducting periodic one-off assessments. For
When it comes to safeguarding web applications from potential threats and vulnerabilities, mastering the art of application threat modeling is essential. Understanding the concept of threat modeling, utilizing tools like STRIDE, implementing best practices in application security, and exploring OWASP tools can significantly enhance the security posture of web applications. This article delves into the intricacies of application threat modeling and its importance in ensuring ultimate web application security.
Understanding the Concept of Threat Modeling
What is a threat model?
A threat model is a structured representation of all the potential security threats and vulnerabilities that could affect a system or application. It involves identifying and prioritizing security risks to develop effective security controls.
Why is threat modeling crucial for web applications?
Threat modeling is crucial for web applications as it provides a systematic approach to identify and address potential security threats. By analyzing the application’s design, architecture, and data flow diagrams, organizations can enhance their security posture and mitigate vulnerabilities.
How does threat modeling enhance application security?
Threat modeling enhances application security by enabling developers to proactively identify and address security threats during the software development lifecycle. It helps in implementing security controls and mitigating potential risks before they are exploited by malicious actors.
Utilizing STRIDE to Identify Potential Threats
What is the importance of STRIDE in threat modeling?
STRIDE is a mnemonic used in threat modeling to categorize different types of security threats: Spoofing, Tampering, Repudiation, Information Disclosure, Denial of Service, and Elevation of Privilege. By using STRIDE, organizations can systematically identify and analyze potential security threats.
How can STRIDE help in recognizing security threats?
STRIDE helps in recognizing security threats by providing a structured framework to evaluate the security implications of each threat type. It assists in prioritizing security concerns and implementing appropriate security measures to mitigate the identified risks.
What are the different aspects covered by STRIDE?
STRIDE covers various aspects of security threats, including identity spoofing, data tampering, information disclosure, denial of service attacks, and unauthorized privilege escalation. Understanding these aspects is crucial for developing effective security controls.
Implementing Best Practices in Application Security
What are the key best practices for securing web applications?
Key best practices for securing web applications include implementing secure coding practices, using encryption for sensitive data, regularly updating software components, conducting security testing, and enforcing access controls. These practices help in reducing vulnerabilities and strengthening application security.
How can security controls mitigate potential threats?
Security controls, such as firewalls, intrusion detection systems, access controls, and secure authentication mechanisms, play a vital role in mitigating potential threats. By implementing these controls based on the identified risks, organizations can effectively protect their web applications from security breaches.
Why is it essential to follow industry best practices in application security?
Following industry best practices in application security is essential to align with established security standards and guidelines. It ensures a proactive approach to addressing security threats and vulnerabilities, thereby enhancing the overall security posture of web applications.
Exploring OWASP Tools for Effective Threat Modeling
What role does OWASP play in web application security?
The Open Web Application Security Project (OWASP) is a non-profit organization dedicated to improving web application security. OWASP provides tools, resources, and knowledge for securing web applications and offers guidance on best practices for threat modeling and vulnerability management.
How can OWASP tools enhance the threat modeling process?
OWASP tools enhance the threat modeling process by offering specialized tools and frameworks tailored for identifying and addressing security threats in web applications. These tools streamline the threat modeling exercise and provide valuable insights into potential security risks.
What are the recommended OWASP tools for threat modeling?
Some of the recommended OWASP tools for threat modeling include OWASP ZAP (Zed Attack Proxy), OWASP Dependency-Check, OWASP Code Pulse, and OWASP WebGoat. These tools assist in identifying vulnerabilities, performing attack simulations, and strengthening the security posture of web applications.
Conducting Threat Modeling Exercises for Enhanced Security
What is the process involved in performing a threat modeling exercise?
The process of performing a threat modeling exercise involves identifying assets, creating a data flow diagram, analyzing potential threats and vulnerabilities, assessing security risks, and implementing security controls. It requires collaboration between developers, security experts, and stakeholders to ensure comprehensive threat assessment.
How can threat modeling techniques help in identifying vulnerabilities?
Threat modeling techniques help in identifying vulnerabilities by systematically analyzing the application’s attack surface, threat actors, and potential attack vectors. By conducting threat modeling exercises, organizations can uncover hidden security risks and take proactive measures to mitigate vulnerabilities.
What are the common types of threats encountered in web applications?
Common types of threats encountered in web applications include SQL injection, cross-site scripting (XSS), security misconfigurations, inadequate authentication mechanisms, and sensitive data exposure. By addressing these threats through effective threat modeling, organizations can enhance the security of their web applications.